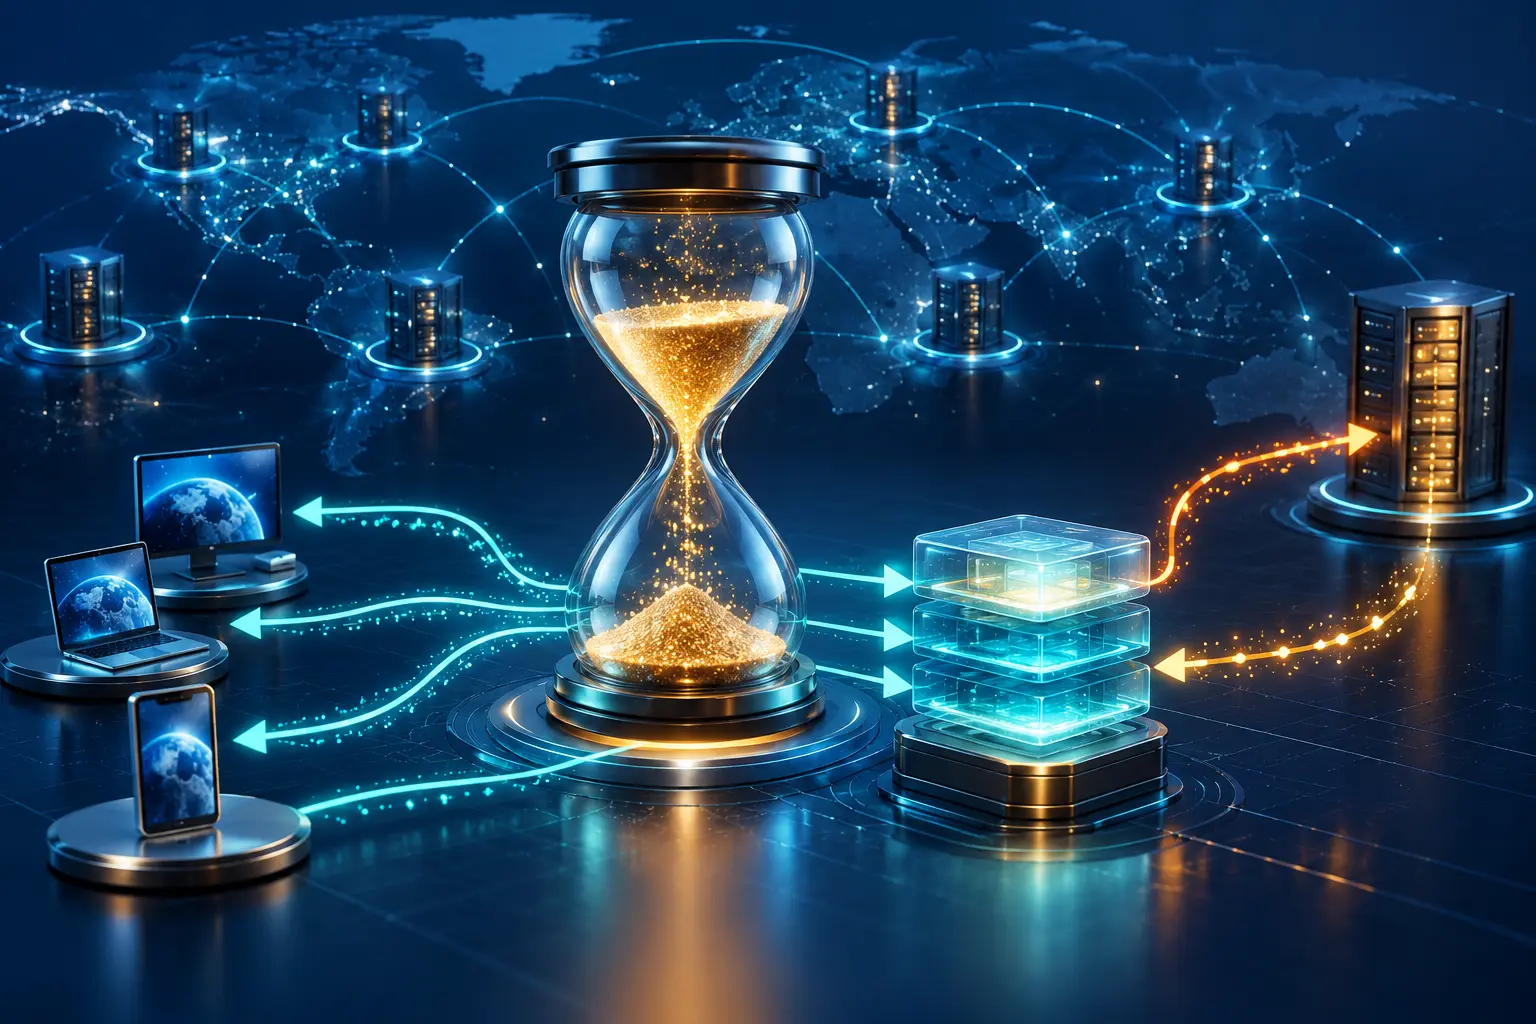
Every DNS record includes a setting that influences how long other systems remember its answer. That setting is the Time to Live, or TTL. It is measured in seconds and tells recursive resolvers how long they may keep a cached DNS response before asking an authoritative DNS server for fresh data.
TTL affects much more than perceived “DNS propagation.” It shapes query volume, response speed, change management, failover behavior, and the load placed on authoritative infrastructure. The best value is therefore a balance: long enough to benefit from caching, but short enough to support the domain’s operational needs.
What happens during the DNS TTL lifecycle?
When a recursive resolver receives a record from an authoritative server, it stores the result together with its TTL. The remaining lifetime counts down while the answer sits in cache. If another user asks for the same record before the timer expires, the resolver can answer from cache without repeating the full lookup.
After the cached value expires, the resolver must obtain an updated answer. This normal caching process is part of the broader resolution flow described in Domain Name System (DNS) explained.
TTL does not instruct every resolver to update at the same instant, and it does not push a new record across the Internet. Different caches learn about a record at different times, so they also expire at different times. Some clients may already have the new answer while others still legitimately use the previous cached value.
Why a longer TTL can be useful
A longer TTL allows recursive resolvers to reuse answers for more time. This provides several practical advantages:
- Fewer authoritative queries. More requests are answered from recursive caches, reducing traffic to authoritative DNS servers.
- Efficient lookups. A cached response avoids repeating the full resolution path and is usually returned quickly.
- Resilience during brief problems. Previously cached records may remain available to users while an authoritative server experiences a short interruption, provided the cached TTL has not expired.
- Predictable operation for stable records. Records that rarely change do not need to be refreshed every few minutes.
The tradeoff is slower adoption of planned changes. If an A or AAAA record has several hours remaining in cache when its authoritative value changes, clients behind that resolver may continue using the old address until the timer reaches zero.
Why a shorter TTL is not always better
A short TTL can make changes visible sooner after cached answers expire, which is useful during a migration or for some automated failover designs. It also causes resolvers to query authoritative servers more frequently. At scale, that can increase DNS traffic and make the quality and geographic reach of the authoritative service more important.
Short values do not guarantee instant switching. Applications, operating systems, local forwarders, browsers, and recursive resolvers can each participate in caching. A low TTL also cannot help clients that already received a longer value before it was reduced. Operational planning matters as much as the final number.
Practical TTL ranges for common situations
There is no universal value that fits every record and every domain. The following ranges are useful starting points, not strict rules:
- Stable website records: 3,600 to 14,400 seconds can provide a reasonable balance when the destination changes infrequently.
- Planned migration: 300 to 900 seconds can reduce the cache window during the change. Lower the TTL early enough for the previous, longer value to expire before migration begins.
- DNS-based failover: 60 to 300 seconds may support faster refreshes, but only when monitoring, authoritative capacity, and recovery procedures are designed for the higher query rate.
- Stable infrastructure records: Values from several hours to a day may be appropriate when the records are carefully managed and rarely changed.
For example, changing a TTL from 86,400 seconds to 300 seconds five minutes before a migration is too late for resolvers that already cached the one-day value. Reduce it at least one full old-TTL period before the planned change. After the migration is confirmed, restore an efficient steady-state value rather than leaving an unnecessarily short TTL forever.
TTL planning for failover and monitoring
TTL is only one part of a failover design. A system must detect the problem, decide whether a change is safe, update the authoritative record, and allow cached answers to expire. A very short TTL cannot compensate for slow detection or an unreliable update process.
This is why DNS monitoring should test both availability and correctness from multiple locations. Teams should also measure authoritative query volume before adopting very short values.
Redundant authoritative infrastructure addresses another part of the problem. A secondary server can continue answering for a zone if the primary becomes unavailable. The architecture and terminology are covered in Get familiar with Secondary DNS. Record TTLs and secondary DNS serve different purposes, but both belong in a complete resilience plan.
Common DNS TTL mistakes
Reducing the TTL too late
The previous TTL remains relevant until every cache holding that response has had time to expire. Schedule the reduction before the maintenance window, not at the moment of the record change.
Using one value for every record
Records have different change patterns and risks. A frequently updated service endpoint may need a shorter value than stable nameserver or verification records. Choose TTLs according to how each record is operated.
Leaving emergency values in place
Teams often reduce TTLs for a migration and forget to raise them afterward. This creates continuous extra query traffic without an ongoing operational benefit.
Treating TTL as a security control
TTL controls cache duration; it does not authenticate an answer or encrypt a query. DNSSEC, protected account access, change auditing, resilient authoritative service, and encrypted transports address separate security concerns.
A simple decision process
- Identify how frequently the record changes during normal operation.
- Define how quickly users must receive a new answer during a planned change or failure.
- Estimate whether the authoritative service can handle the resulting query rate.
- Lower the TTL in advance of maintenance and wait for the old cache window to pass.
- Monitor the change from multiple networks and restore the steady-state TTL afterward.
For a broader operational checklist, see DNS best practices. The original DNS protocol specification defines the TTL field and caching behavior in RFC 1035: Domain Names—Implementation and Specification.
Conclusion
A well-chosen DNS TTL supports both efficiency and controlled change. Longer values reduce repeated authoritative lookups, while shorter values narrow the cache window when records must change quickly. The right approach is to use stable defaults, lower values deliberately before planned work, monitor the results, and return to an efficient setting when the event is complete.